What Is Multichain Bridging? How Crypto Bridges Work and Why They Get Hacked
On this page
I've been reading the latest news about all the hacking that has been going on in the multichain universe. However, I'm still struggling to understand exactly what it is. Can anyone share?
The short answer
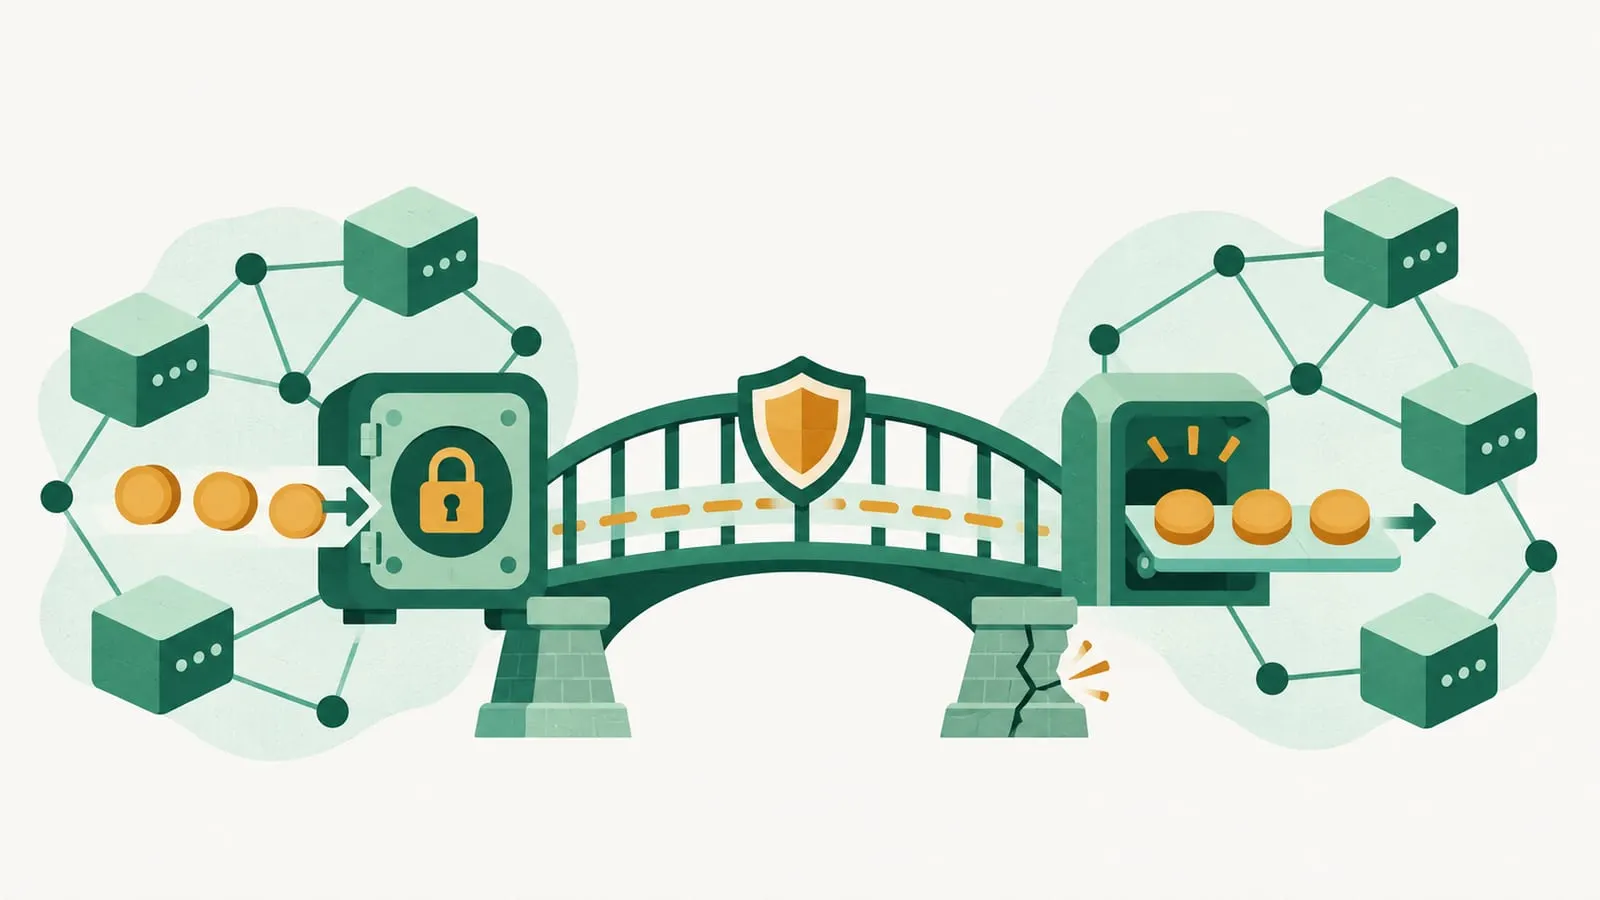
Multichain bridging means moving crypto assets, or messages, from one blockchain to another using a bridge. Blockchains cannot read each other’s state, so a bridge acts as the go-between. In the most common design, your tokens are locked in a contract on the source chain and an equivalent wrapped token is minted on the destination chain. When you go back, the wrapped token is burned and the original is unlocked.
The hacks you have been reading about happen because those locked pools become enormous honeypots, often protected by a handful of keys or a single smart contract. Get past that protection and an attacker can drain everything the bridge holds.
“Multichain” is also the name of a specific bridge, formerly called Anyswap, which collapsed in July 2023. More on that below.
Why bridges are needed
Each chain is its own ledger. ETH on Ethereum cannot simply appear on Avalanche or Solana, and a token on Arbitrum is not automatically usable on Base. Users bridge to:
- Use apps or lower fees on another chain, such as moving stablecoins to a layer 2.
- Use an asset where it doesn’t natively exist, for example BTC in Ethereum DeFi via wrapped Bitcoin.
- Move liquidity to wherever yields or opportunities are.
For the broader concept, see what cross-chain means in DeFi and why interoperability matters.
How bridges work: the main designs
| Design | How it works | Examples (illustrative) | Main risk |
|---|---|---|---|
| Lock and mint | Lock the original on chain A, mint a wrapped token on chain B | Many early bridges, wrapped BTC | The lock-up pool can be drained; wrapped token depends on it |
| Burn and mint | Burn on chain A, mint natively on chain B; usually run by the token issuer | Circle’s CCTP for USDC | Trust in the issuer; no separate pool to drain |
| Liquidity networks | Liquidity providers on each chain pay you out; no wrapped token | Hop, Connext | Liquidity limits; relayer and contract risk |
| Native / canonical bridges | A rollup’s official bridge, secured by the rollup itself | Arbitrum and Optimism bridges | Slow withdrawals on optimistic rollups (about 7 days) |
| Message-passing protocols | Pass arbitrary messages and tokens between chains | LayerZero, Axelar, Wormhole, Chainlink CCIP | Depends on the verifier set and configuration |
ethereum.org groups these into two families:
- Trusted bridges rely on an external set of verifiers, such as a multisig, an MPC key or an oracle network. They are usually fast and cheap, but you are trusting those operators.
- Trust-minimized bridges rely on the connected chains themselves, using light clients or fraud and validity proofs. They add fewer trust assumptions but are often slower or more limited.
Many apps now hide this behind “intents”: you say what you want on the destination chain and a solver or relayer delivers it, settling with the bridge later. It is faster, but the underlying security still depends on how settlement works.
Why bridges get hacked
Bridges have long been among the largest targets in DeFi. Chainalysis estimated that by August 2022, about $2 billion had been stolen in 13 cross-chain bridge hacks that year, about 69% of all funds stolen in crypto up to then.
| Bridge | Date | Approx. loss | What went wrong (simplified) |
|---|---|---|---|
| Ronin (Axie Infinity) | March 2022 | ~$624M | Attackers obtained five of nine validator keys and approved withdrawals of about 173,600 ETH and 25.5M USDC |
| Poly Network | August 2021 | ~$611M | Contract flaw let the attacker change who could authorize transfers; most funds were returned |
| BNB Bridge | October 2022 | ~$586M | Flaw in proof verification let the attacker mint 2 million BNB; BNB Chain was halted and most of it never left the chain; Binance’s early estimate was that about $100M was moved off |
| Wormhole | February 2022 | ~$326M | Signature-verification bug let the attacker mint wrapped ETH without collateral |
| Nomad | August 2022 | ~$186M–$190M | Faulty upgrade let anyone copy a valid transaction and withdraw funds; hundreds of copycat addresses joined in |
| Kelp DAO rsETH (LayerZero route) | April 2026 | ~$292M | A single verifier (a “1-of-1” setup) approved a forged cross-chain message, releasing 116,500 rsETH with no matching burn on the source chain; lenders that accepted rsETH, including Aave, were left with bad debt |
| Liquid (Bitcoin sidechain) | September 2026 | ~$320M | About 4,000 BTC, roughly 95% of the federation’s reserve, was withdrawn after unbacked L-BTC was created through a bug in the Elements software and redeemed through a member’s peg-out service. Blockstream’s assessment says no key was compromised but that one member, SideSwap, kept its peg-out signing key online contrary to the federation charter, which SideSwap acknowledged; SideSwap’s developers have emphasised the software flaw. The attackers returned about 3,400 BTC and described the roughly 600 BTC they kept as a “bounty” |
Loss figures come from Rekt’s leaderboard, Chainalysis, Coinbase’s Nomad analysis and Aave’s rsETH incident report, and estimates vary between sources (Rekt lists Kelp at $290 million). Common causes are compromised keys, bugs in signature or proof checks, weak verifier configurations and bad upgrades. The Kelp case shows that the risk spreads: lending markets that accepted the bridged token as collateral took losses even though their own contracts worked as designed. These are classic smart contract vulnerabilities and operational failures, made worse because a single bridge may hold hundreds of millions of dollars.
What happened to Multichain
Multichain, originally Anyswap, was one of the most widely used bridges, connecting dozens of chains. It used MPC (multi-party computation) wallets, which were meant to spread control of the keys. In practice:
- Its CEO, known as Zhaojun, was detained by Chinese police in May 2023, and the bridge began failing.
- On July 6, 2023, about $126 million moved out of Multichain’s wallets in what the team called “abnormal” transfers, most of it from its Fantom bridge. Multichain announced it was ceasing operations on July 14.
- Multichain then ceased operations, saying the team’s funds and server access were with the CEO, who had been in custody since May 21, and the police.
Whether it was a hack or an insider job has never been fully settled. In 2024 a Singapore court granted the Fantom Foundation (now Sonic Labs) a default judgment against Multichain Foundation for breach of contract and fraudulent misrepresentation, and the court later ordered the foundation wound up. Users holding Multichain-bridged tokens, especially on Fantom, were left with tokens that had lost their backing. The lesson: “decentralized” labels mean little if one person can control the keys.
How to bridge more safely
- Prefer native routes. Use an issuer’s own transfer system (such as CCTP for USDC) or a rollup’s official bridge when you can. Our guide to low-fee stablecoins explains bridged versus native stablecoins.
- Check how the bridge is secured. How many signers, who they are, whether it uses a multisig, MPC or proofs, whether it is audited and how long it has run without incident.
- Use the real URL. Bookmark official sites; phishing clones of bridges are common.
- Know which token you’ll receive. A bridge-specific wrapped token is not the same as the native asset and may have less liquidity.
- Move only what you need, and test first with a small amount.
- Don’t leave large balances in bridged assets long-term if a native version exists.
- Consider an exchange as an alternative. Depositing on one chain and withdrawing on another swaps bridge risk for exchange counterparty risk.
Risks summary
- Smart-contract and key compromise can drain the bridge and devalue every wrapped token it issued.
- Centralization: a small validator set or single operator can fail or act maliciously.
- Depeg risk: bridged tokens can trade below the original if confidence in the bridge drops.
- Stuck transfers: congestion, paused bridges or wrong-network sends can leave funds in limbo.
- Irreversibility: a transfer sent to the wrong chain or address usually cannot be undone; see why transactions are irreversible.
For more, see the multichain bridging and cross-chain glossary entries, or the DeFi basics guide.
Frequently asked questions
Is Multichain still working?
No. Multichain (formerly Anyswap) ceased operations in July 2023 after abnormal outflows of about $126 million and the detention of its CEO in China. Do not use sites claiming to be Multichain.
Are bridged tokens the same as native tokens?
No. A bridged token is a claim on assets locked by the bridge. If the bridge is hacked or its locked reserves are drained, the bridged token can lose its value even though the original asset is fine.
What is the safest way to move tokens between chains?
There is no zero-risk option. Issuer-native transfers (such as Circle's CCTP for USDC) and a rollup's official bridge avoid an extra custodian, while centralized exchanges let you deposit on one chain and withdraw on another, swapping bridge risk for exchange risk.
How long does bridging take?
From seconds to days. Liquidity and intent-based bridges can deliver in seconds or minutes; withdrawals from optimistic rollups through their official bridge take about a week because of the challenge period.
What is the difference between cross-chain and multichain?
The terms overlap. 'Multichain' usually describes an app or token deployed on many chains, while 'cross-chain' describes moving assets or messages between them. Bridges are the infrastructure that makes cross-chain transfers possible.
Sources
- Ronin: Back to Building, Ronin security breach post-mortem (April 2022)
- Changpeng Zhao on X: BSC Token Hub exploit impact estimate (October 6, 2022)
- BNB Chain: BNB Chain Ecosystem Update (October 7, 2022)
- ethereum.org: Introduction to blockchain bridges
- Chainalysis: Cross-chain bridge hacks in 2022
- Rekt: Leaderboard of largest DeFi hacks
- Coinbase: Nomad Bridge incident analysis (2022)
- Aave governance forum: rsETH Incident Report (April 20, 2026)
- SiliconANGLE: Hackers steal $320M in bitcoin from Liquid Network, return most of it (September 2026)
- Blockstream: Liquid Network security incident assessment (September 23, 2026)
- Chainalysis: How the $320M exploit of Liquid Network went down
- Singapore High Court: Fantom Foundation v Multichain Foundation [2024] SGHC 173
- DL News: Multichain halts bridge, says CEO arrested (July 2023)
- Circle: Cross-Chain Transfer Protocol (CCTP) documentation
Educational content, not financial advice. DeFi carries risk, including total loss of funds.