What Is a Multisig Wallet? How Multi-Signature Wallets Work
On this page
What is a multisig wallet?
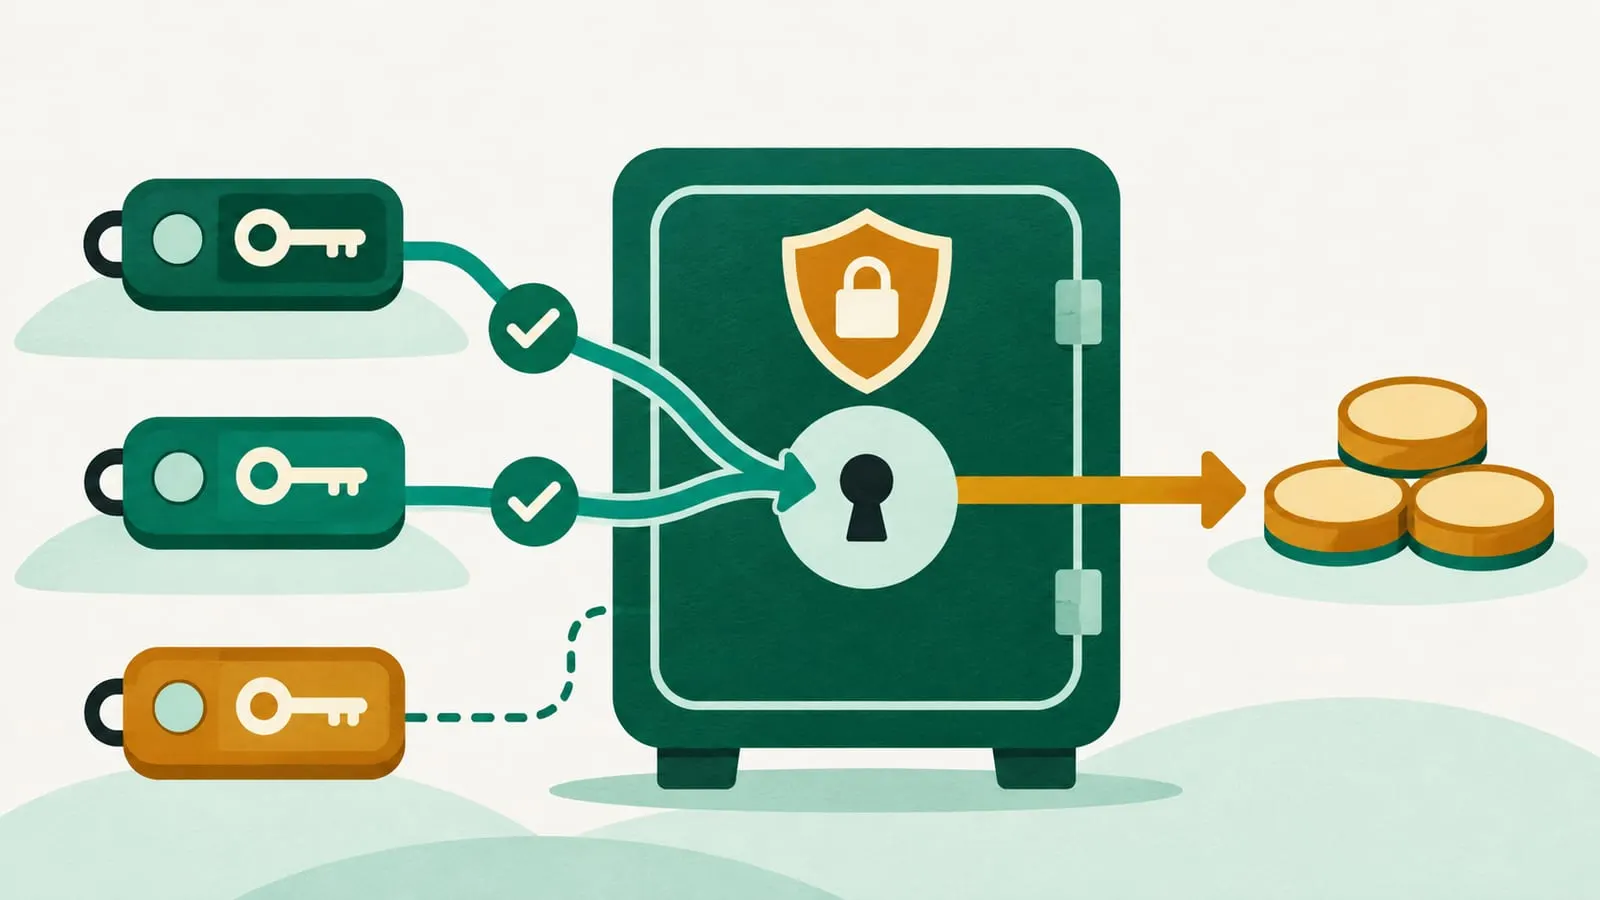
A multisig wallet (short for multi-signature wallet) is a crypto wallet that needs approval from more than one private key before it can send funds. It is set up as M-of-N: there are N authorized keys, and any M of them must sign. In a 2-of-3 multisig, for example, three keys exist and any two can approve a transaction.
A normal wallet has one private key, usually backed up as one seed phrase. Whoever has that key controls the funds, and losing it means losing access. A multisig removes that single point of failure.
How a multisig wallet works
- Setup. The owners choose the keys (each usually on a separate device, often a hardware wallet) and the threshold, such as 2-of-3 or 3-of-5.
- Proposal. One owner creates a transaction, for example “send 10 ETH to this address”.
- Signing. Other owners review and sign it on their own devices until the threshold is reached.
- Execution. Once enough valid signatures are collected, the transaction is broadcast and the funds move.
How the rule is enforced depends on the chain:
- Bitcoin supports multisig natively in its scripting system, and Taproot made complex spending conditions cheaper and more private. Wallets such as Sparrow, Electrum and Nunchuk support it, as do collaborative-custody services.
- Ethereum and EVM chains have no built-in multisig, so it is a smart contract account. Safe (formerly Gnosis Safe) is the standard; Safe says it secures more than $60 billion of assets across 40+ networks. Because it is a contract, it can add spending limits, modules and recovery rules.
- Solana programs such as Squads provide the equivalent.
Common multisig setups
| Setup | Typical use | Why |
|---|---|---|
| 2-of-3, one person | Personal savings | Keys on two hardware wallets plus a backup in another place; one lost or stolen key is survivable |
| 2-of-3 with a service | Collaborative custody, inheritance | You hold two keys, a provider holds one for recovery but cannot move funds alone |
| 3-of-5 or larger | DAO treasuries, company funds | No single team member can move money |
| Admin multisig | Protocol upgrades and emergency pauses | Spreads control of powerful admin keys, often paired with a timelock |
| 2-of-2 escrow | Trades between two parties | Funds move only when both agree, sometimes with an arbiter’s third key |
DAOs commonly hold treasuries this way; see how DAOs work. When you assess a protocol, who holds its admin multisig and how many signatures it needs are key questions, as our guide to smart contract vulnerabilities explains.
Advantages
- No single point of failure. One phished, lost or broken key does not lose the funds.
- Shared control. Partners, teams and DAOs can require agreement before spending.
- Built-in recovery and inheritance. A spare key held by family, a lawyer or a service can help recover funds without giving anyone sole access.
- Programmable rules on smart contract multisigs, such as daily limits or delays.
Risks and limitations
A multisig only checks that enough people signed. It cannot tell whether they understood what they signed. The largest multisig losses have come from that gap:
- Bybit, February 2025: attackers compromised a Safe{Wallet} developer’s machine and tampered with the web interface Bybit used. Bybit’s signers saw a normal-looking transfer but signed a transaction that handed control of a cold wallet to the attackers, who took about $1.4–1.5 billion, depending on the estimate.
- Radiant Capital, October 2024: about $50 million was lost through social engineering and blind signing, according to Radiant’s own post-mortem and DefiLlama’s hacks database (Rekt lists $53 million): signers approved transactions that did not do what they appeared to.
- Drift Protocol, April 2026: Drift’s Security Council used a 2-of-5 multisig on Solana. Attackers obtained approvals in advance, reportedly through months of social engineering and misrepresented transactions, using Solana “durable nonce” transactions that do not expire. They executed them on 1 April and took admin control, withdrawing about $285 million (DefiLlama lists $295 million). See risks of yield farming.
Other limitations:
- Complexity. More keys mean more backups to manage. Fall below the threshold and the funds are locked forever.
- Smart contract risk. Contract-based multisigs rely on their code; in November 2017 a flaw in a shared Parity multisig library froze funds in many multisig wallets, including about 306,000 ETH belonging to the Web3 Foundation.
- Cost and support. Each signature can cost gas, and not every app or chain supports every multisig.
Good practice: keep each key on a separate hardware wallet, check the transaction details on the device screen rather than only in the web app, use a threshold above two for large or shared funds, add a timelock to admin actions, and test recovery with a small amount first.
Multisig vs. MPC vs. single-key wallets
| Single-key wallet | Multisig | MPC wallet | |
|---|---|---|---|
| Keys | One | Several complete keys | One key split into shares |
| Where the rule is enforced | n/a | On-chain (script or contract) | Off-chain, by the signing software |
| Visible on-chain | Normal address | Multisig script or contract | Looks like a normal address |
| Main weakness | Lose or leak one key, lose everything | Setup complexity; signers approving bad transactions | Trust in the provider’s software |
For where multisig fits among other wallet types, see what a DeFi wallet is and hot vs. cold wallets, or browse the wallets and security section.
Frequently asked questions
What does 2-of-3 multisig mean?
There are three authorized keys, and any two of them must sign for a transaction to go through. Losing one key, or having one stolen, does not by itself lose or expose the funds.
Is a multisig wallet safer than a hardware wallet?
They solve different problems and are often combined. A hardware wallet protects one key; a multisig spreads control across several keys, ideally each on its own hardware wallet held by different people or in different places.
What is the difference between multisig and MPC wallets?
A multisig uses several complete keys and the blockchain or a smart contract checks each signature. An MPC wallet splits one key into shares that jointly produce a single ordinary signature off-chain, so on-chain it looks like a normal wallet.
What happens if I lose one key in a multisig?
If enough keys remain to meet the threshold, you can still move the funds and should replace the lost key. If you fall below the threshold, the funds are locked permanently.
Sources
- TRM Labs: North Korean hackers attack Drift Protocol in $285 million heist (April 2026)
- Radiant Capital: Radiant post-mortem (October 2024)
- Safe documentation: What is Safe?
- Safe: Smart account platform
- The Block: Lazarus appears to compromise Safe developer machine in lead-up to $1.5 billion Bybit hack
- CoinDesk: How a Solana feature designed for convenience let attackers drain Drift (April 2026)
- DefiLlama: Hacks database
Educational content, not financial advice. DeFi carries risk, including total loss of funds.